XML-RPC is a legacy WordPress protocol that allows remote publishing and app integrations but has since been replaced by the more secure and flexible REST API. Despite this, XML-RPC remains enabled by default and is often exploited for brute-force logins and DDoS amplification. If you’re not using tools like Jetpack or the WordPress mobile app, it’s best to disable XML-RPC to reduce security risks.
Check If XML-RPC is Enabled in Your Website
Go to this address: https://your-website-url.com/xmlrpc.php, for example, https://taiht.dev/xmlrpc.php.
If you see this message:
XML-RPC server accepts POST requests only.Code language: plaintext (plaintext)Then XML-RPC is enabled in your website.
How to Disable XML-RPC
You can disable XML-RPC in several ways depending on your environment setup. Choose one of the methods below, or combine them for stronger security.
Method 1: Disable XML-RPC in the web server (Nginx or Apache)
For Nginx, add this code to the server block:
## Block all requests to /xmlrpc.php
location = /xmlrpc.php {
    deny all;
    access_log off;
    log_not_found off;
}
Code language: Nginx (nginx)
For Apache, add this code to .htaccess file:
<Files "xmlrpc.php">
    Require all denied
</Files>Code language: Apache (apache)
Method 2: Block all requests to XML-RPC on Cloudflare
If your site sits behind Cloudflare, you can block all requests to xmlrpc.php file at the edge. This method not only improves security but also reduces server load. To do this, go to your Cloudflare dashboard, then:
- Choose your website → Security → Security rules.
- Hit the Create rule button → Custom rules.
- Set up the rule as in the picture below:
- Field:
URI Path - Operator:
contains - Value:
xmlrpc.php - Then take action:
Block
- Field:
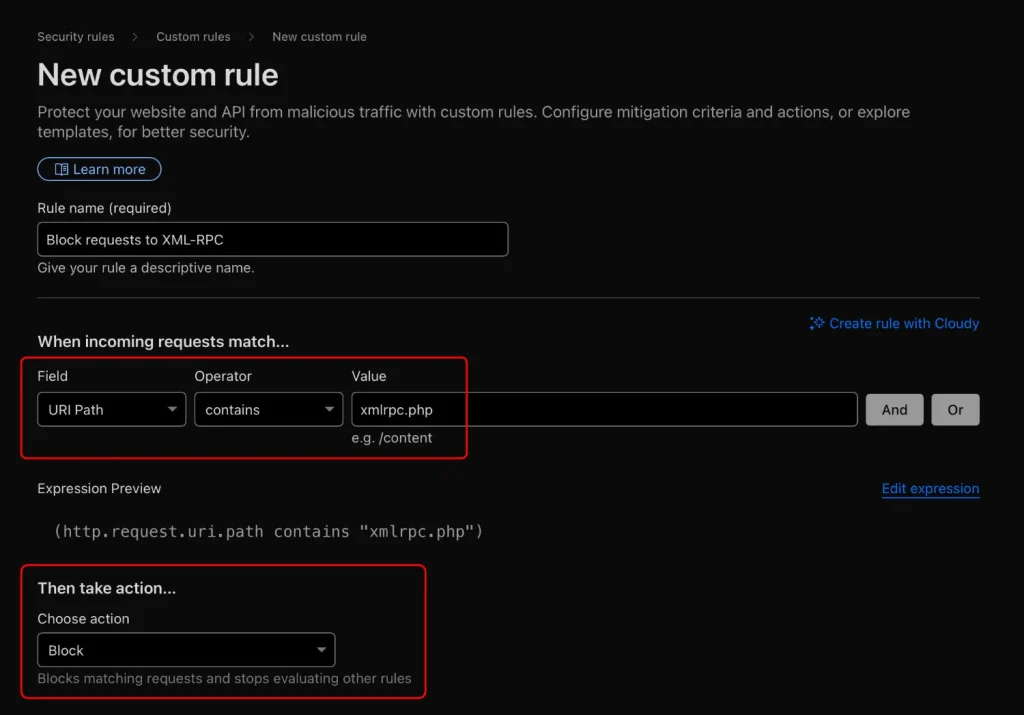
With this rule in place, any request containing xmlrpc.php in the URL will be blocked instantly before it reaches your server. Now your site is protected from XML-RPC attacks and also saving server resources, which help improving overall performance.